Cybersecurity · Free
ISO 27001:2022 Implementation: Build an ISMS
Build an information security management system to ISO/IEC 27001:2022, step by step: context, interested parties and scope, leadership and policy, risk assessment and risk treatment, the Statement of Applicability, the 93 Annex A controls in four themes, documented information and evidence, supplier, cloud, incident and continuity controls, internal audit and management review, corrective action, the stage 1 and stage 2 certification audits, and how the ISMS maps to GDPR, NIS2, SOC 2 and NIST CSF 2.0.
Inside the course
From the lessons

ISO 27001 and the ISMS: what the standard asks for
Dejan Kosutic

Clause 4: context, interested parties and the ISMS scope
Consultants Like Us

Clause 6.1.2: risk criteria and the information security risk assessment
URM Consulting

Annex A and ISO/IEC 27002:2022: 93 controls in four themes
NQA Certification

People, physical and technological controls in practice
Stuart Barker

Clause 9: monitoring, internal audit and management review
Consultants Like Us
Lesson frames belong to the creators named in the Credits below and are shown from YouTube.
What you will learn
Plan an ISO 27001 implementation as a project with a gap analysis; set the ISMS scope from the context, interested parties and interfaces, including the 2024 climate amendment; write an information security policy and assign roles; define risk criteria, run a risk assessment and calculate risk levels; choose treatment options and write the risk treatment plan; build a Statement of Applicability with a justification for every Annex A control; apply organisational, people, physical and technological controls; control documented information and keep the evidence an auditor samples; run an internal audit and a management review; write corrective actions from root causes; prepare for the stage 1 and stage 2 certification audits; and map the ISMS to GDPR, NIS2, SOC 2 and NIST CSF 2.0.
- Plan an ISO 27001:2022 implementation with a gap analysis and a phased roadmap
- Write the context, interested parties and a credible ISMS scope, including the 2024 climate amendment
- Set risk criteria, run a risk assessment and calculate risk levels against an acceptance threshold
- Choose risk treatments and build a Statement of Applicability that justifies every Annex A control
- Apply the 93 Annex A controls across organisational, people, physical and technological themes
- Control documented information and keep the records an auditor samples
- Run an internal audit and a management review, and write corrective actions from root causes
- Prepare for stage 1 and stage 2 certification audits and map the ISMS to GDPR, NIS2, SOC 2 and NIST CSF 2.0
For you
Taking ISO 27001:2022 Implementation: Build an ISMS from the United States
- Free in the United States, as everywhere, and self-paced: lessons, notes and the final assessment are open at any hour, so your time zone and shift pattern do not matter.
- The optional certificate for learners in the United States is a one-off US$28.99. What you get for it
- Plants across the Americas most often run Allen-Bradley, Siemens and Inductive Automation; each has its own free course to take next.
- See automation and engineering jobs in the United States, and what the industry looks like in Houston, Detroit and Chicago.
- EDWartens also has a regional site for the United States, for classroom training and local support: edwartens.com/us.
The course project · about 14 hours
ISMS starter pack for a SaaS analytics company: scope, risk register, Statement of Applicability, audit procedure and audit report
Act as the ISMS lead for an 85-person software company that must be ready for an ISO/IEC 27001:2022 stage 1 audit in six months. Write the scope and context statement, run the risk assessment, build the Statement of Applicability, write the internal audit procedure, and audit one area and report the findings. The sample pack shows each document for a fictional company, Harbourline Analytics.
Sample document pack, 5 documents, filled in for the scenario
- PlanISMS scope and context statement
- Risk registerInformation security risk register
- RegisterStatement of Applicability (extract)
- ProcedureInternal audit procedure
- ReportInternal audit report: access control
Read inside the course and download as a workbook. The project is optional practice, marked when you submit it; the certificate needs only the modules and the final assessment.
Course content
14 modules · 40 lessons · 13h 20m
In order, at whatever pace suits you. Each module ends with a practice task that builds on the last.
- 01ISO 27001 and the ISMS: what the standard asks for3 lessons28m
- 02The implementation roadmap: project, gap analysis and the 2022 changes3 lessons1h 30m
- 03Clause 4: context, interested parties and the ISMS scope3 lessons1h 20m
- 04Clause 5: leadership, the security policy and roles3 lessons40m
- 05Clause 6.1.2: risk criteria and the information security risk assessment3 lessons1h 25m
- 06Clause 6.1.3 to 6.3: risk treatment, the SoA, objectives and planning changes3 lessons1h 12m
- 07Annex A and ISO/IEC 27002:2022: 93 controls in four themes3 lessons1h 4m
- 08Organisational controls: suppliers, cloud, incidents and continuity4 lessons46m
Requirements
- Who it is for
- Intermediate. For IT, security, compliance, quality and operations staff, consultants and graduates who will help an organisation implement or maintain ISO/IEC 27001. Basic IT and security vocabulary helps; no previous management system experience is needed. Cybersecurity Fundamentals for Beginners is a good first step if you are new to security.
- Software
- A spreadsheet (LibreOffice Calc or Google Sheets is free) for the risk register and the Statement of Applicability, and a document editor for policies and procedures. You do not need to buy the standard to follow the course, but anyone implementing it for real should hold a licensed copy of ISO/IEC 27001:2022 and its 2024 amendment. What to download, and how
- Hardware
- None.
Software you need
What to download, where from, what it costs and how to install it. Every link goes to the maker's own site, never a mirror.
Nothing to install
A spreadsheet and a document editor are enough; Google Sheets or LibreOffice Calc are free. For real implementation work, buy a licensed copy of ISO/IEC 27001:2022 and its 2024 amendment from ISO or your national standards body.
Optional
Useful, not needed to finish the course.
- 01Free
LibreOffice
The Document Foundation
- Runs on
- Windows 10 or 11, macOS 11 or newer (Intel or Apple silicon), Linux
- Account
- None needed
- Size
- up to 1.5 GB of disk space on Windows
LibreOffice is free, open-source software under the Mozilla Public License 2.0, for any use including business. Calc is its spreadsheet.
Steps
- 1.Open the LibreOffice download page.
- 2.Check the page has picked your operating system, then select Download.
- 3.Run the installer (administrator rights are needed on Windows).
- 4.Start LibreOffice Calc for spreadsheet work.
- 5.Save as .xlsx if you need to share files with Excel users.
- Choose the latest main version unless your organisation asks for the older, more conservative release.
Official download pagelibreoffice.org
Checked against each maker's own page on 27 September 2026. Trial lengths and editions change; the maker's page is the final word.
ISO 27001:2022 Implementation: Build an ISMS at a glance
ISO 27001:2022 Implementation: Build an ISMS is a free, self-paced online course from EDWartens for IT, security, compliance and quality staff, consultants and graduates who will implement or maintain an ISO/IEC 27001 information security management system. It has 14 modules and 13h 20m of video lessons by Dejan Kosutic, Consultants Like Us, Stuart Barker and others, with written notes and worked problems, a practical project with a document pack and a 15-question final assessment (pass mark 60%). Learning is free with an account; an optional certificate with a public verification code is issued when you pass. Last updated 27 September 2026.
All course factsHide course facts
- Price
- Free, for good. No trial, no card. The only paid item is the optional certificate, a small one-off fee.
- Who it is for
- IT, security, compliance and quality staff, consultants and graduates who will implement or maintain an ISO/IEC 27001 information security management system
- Format
- 14 self-paced modules, 13h 20m of video, written notes, a practice task per module and one final assessment.
- Level
- Intermediate. Intermediate. For IT, security, compliance, quality and operations staff, consultants and graduates who will help an organisation implement or maintain ISO/IEC 27001. Basic IT and security vocabulary helps; no previous management system experience is needed. Cybersecurity Fundamentals for Beginners is a good first step if you are new to security.
- Brand
- Vendor-neutral
- Software
- A spreadsheet (LibreOffice Calc or Google Sheets is free) for the risk register and the Statement of Applicability, and a document editor for policies and procedures. You do not need to buy the standard to follow the course, but anyone implementing it for real should hold a licensed copy of ISO/IEC 27001:2022 and its 2024 amendment.
- Hardware
- None.
- Certificate
- Optional EDWartens Certificate of Completion, verifiable by code. Not a vendor credential.
- Video lessons by
- Dejan Kosutic, Consultants Like Us, Stuart Barker, Prabh Nair, URM Consulting, CertiKit, NQA Certification, risk3sixty, SoftComply, GRC Made Simple (independent creators, credited below)
- Language
- English
- Last updated
- 27 September 2026
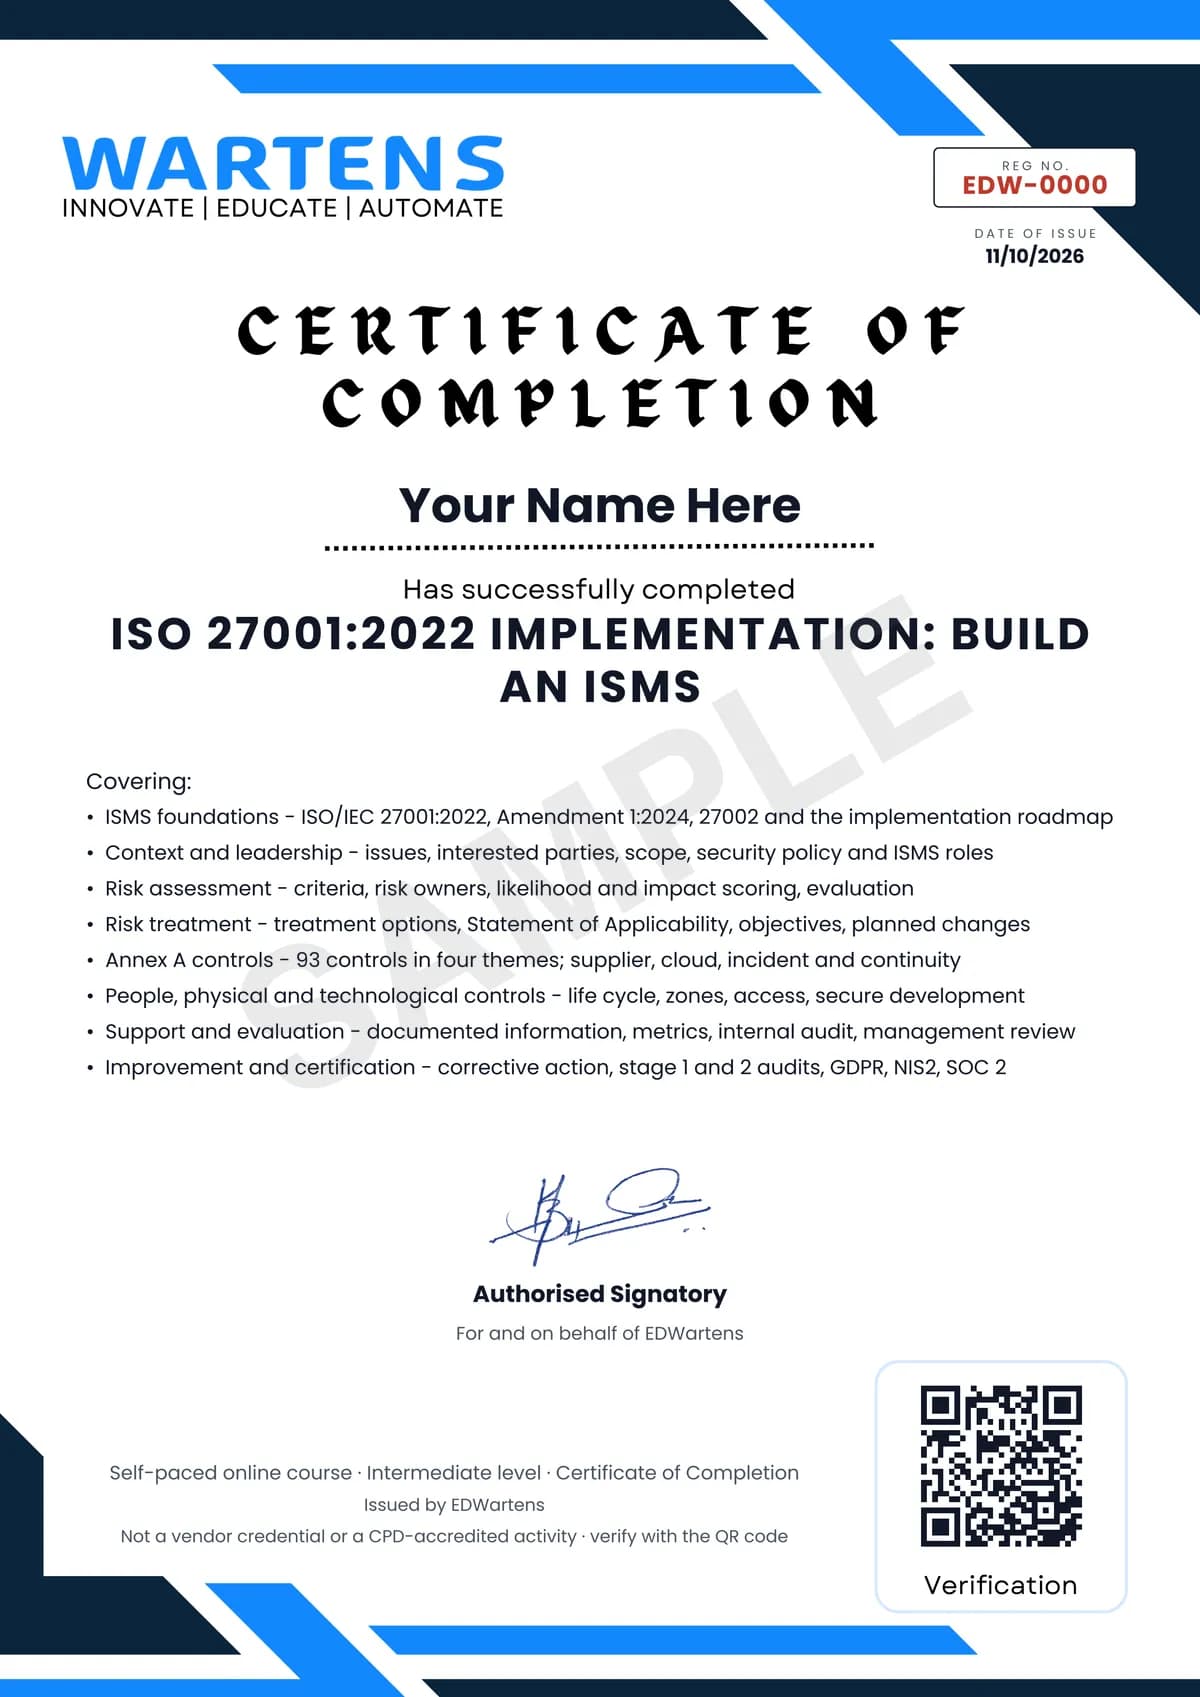
A shareable EDWartens certificate
Finish every module and pass the final assessment, and the optional EDWartens certificate is yours. It carries a unique verification code on a public page anyone can check, so it stands up when a recruiter looks it up. See it below.
The course itself stays free whether or not you ever buy one.
Stuck? Ask a practising engineer
A free course usually means a comment section and hope. This one does not. Every module has an Ask-your-trainer panel that reaches the same engineers who teach our paid programme: people who commission panels for a living, not moderators.
Pairs well with
 FreeCybersecurity · FreeCompTIA Security+ (SY0-701) Exam PrepPrepare for CompTIA Security+ SY0-701 with Professor Messer's complete free video course: every exam objective across the five domains, with EDWartens notes, worked calculations, practice questions and an optional security project. Exam preparation only: the EDWartens certificate is not the CompTIA Security+ certification, which is earned only by passing CompTIA's exam.
 FreeCybersecurity · FreeMicrosoft Sentinel and Defender: SC-200 Exam PrepPreparation for Microsoft's SC-200 Security Operations Analyst exam, mapped to the skills measured as of 21 October 2026: KQL from first query to hunting, Microsoft Defender XDR incidents and attack disruption, Defender for Endpoint, Office 365, Identity and Cloud Apps, Purview investigations, Microsoft Sentinel setup, data connectors, analytics rules, automation, Security Copilot and threat hunting.
 FreePLC programming · FreeSiemens TIA PortalFree Siemens TIA Portal course for beginners: write ladder logic for a simulated S7-1200 and WinCC HMI. Learning is free; the certificate is optional and paid.
 FreePLC programming · FreeSiemens TIA Portal in Three HoursThe first three hours of the Siemens TIA Portal course, cut to end on a win: what a PLC is, how it is wired, a project configured in TIA Portal, and your first ladder program running in simulation. Finish it in an evening or two, earn a certificate, and carry straight on into the full course.
More free courses: Free cyber security courses
Learner reviews
No reviews yet
Reviews here are written only by learners who have finished every module of ISO 27001:2022 Implementation: Build an ISMS, and they are published exactly as written. Finish the course and yours will be the first.
Common questions
What is the ISO 27001 implementation course?
It is a free-to-learn course that shows you how to build an information security management system (ISMS) to ISO/IEC 27001:2022, step by step: context and scope, leadership and policy, risk assessment and treatment, the Statement of Applicability, the 93 Annex A controls, documented information, internal audit, management review, corrective action and the stage 1 and stage 2 certification audits.
Who is this ISO 27001 course for?
IT and security staff, compliance and quality officers, consultants and graduates who will implement or maintain an ISMS, and managers who have been asked to get their organisation certified. Basic IT and security vocabulary helps; no previous ISO management system experience is needed.
Which version of ISO 27001 does the course teach?
ISO/IEC 27001:2022 with Amendment 1:2024 (climate action changes), which was the current version when the course was checked on 11 October 2026; the transition from the 2013 edition ended on 31 October 2025. The course also uses ISO/IEC 27002:2022 for the controls and ISO/IEC 27005:2022 for risk, and paraphrases the standards rather than reproducing their text.
What is a Statement of Applicability in ISO 27001?
The Statement of Applicability (SoA) is the document that lists every Annex A control, says whether it applies, justifies including or excluding it, and records whether it is implemented. The course shows how to build it from the risk treatment decisions so that each row points to a risk, a contract or a legal requirement.
Is this an ISO 27001 lead implementer or lead auditor certification?
No. The course covers the knowledge used in implementation and internal audit work, but its certificate is a verifiable certificate of completion from EDWartens, not a lead implementer or lead auditor credential, and it does not certify any organisation. Organisations are certified by independent certification bodies.
How long does the course take, and is it free?
About 13 hours of video and around 19 hours in total with the notes, worked problems and practice tasks, at your own pace. Every module, the notes, the optional ISMS starter-pack project and the final assessment are free to learn.
What certificate does the ISO 27001:2022 Implementation: Build an ISMS course give?
A verifiable certificate of completion, issued when you finish the modules and pass the 15-question final at 60 percent. It has a unique certificate number, a QR code and a public verification page that shows the course, the modules covered and your final score.
What jobs does ISO 27001 implementation knowledge lead to?
It is the core knowledge for roles such as ISMS coordinator, information security officer, GRC analyst, compliance analyst and internal auditor, and it supports consultants who help companies prepare for certification. Suppliers to banks, governments and large enterprises are often required to hold ISO/IEC 27001.
What you walk away with
Your certificate for ISO 27001:2022 Implementation: Build an ISMS
Finish the course, pass the final, and this is the document with your name on it.
Verifiable by anyone
Adds to LinkedIn in one click
QR code on the certificate
Names what you can do
A permanent link
Earned, not attended
Learning is free. The certificate is optional.
Add it now and pay only when you have finished the course, or come back for it later. One-off, US$28.99, with a receipt.
Issued by EDWartens, the training division of Wartens, as a Certificate of Completion for this self-paced course. Sold by Wartens Ltd (England and Wales). It is not a vendor certification, a university award or a CPD-accredited activity, and it does not certify competence on live equipment. Delivered electronically; see the refund policy.
Credits
Who made the video lessons
The video lessons in this course were created by the people below, not by EDWartens. Every lesson streams from its creator's own YouTube channel; EDWartens neither hosts nor sells that footage, and the creators are not affiliated with EDWartens and do not endorse this course. What EDWartens wrote is the study plan, the notes, the practice tasks and the assessments.
- Dejan Kosuticthe Advisera lessons on what ISO 27001 is, the clauses, the seven implementation steps, setting the scope, risk assessment and treatment, writing the Statement of Applicability, implementing Annex A controls and internal audit essentials
- Consultants Like Usthe clause-by-clause explanations of clauses 4 to 9, the information security policy and mandatory policies, the Annex A lessons on supplier relationships, cloud services, incident management planning, ICT readiness and the secure development life cycle, and preparing for the stage 1 and stage 2 audits
- Stuart BarkerISO 27001 and ISO 27002 compared, implementing clause 4, management review, continual improvement, and the Annex A lessons on remote working and user endpoint devices
- Prabh Nairthe end-to-end implementation case study, the project initiation document, building a Statement of Applicability from scratch and writing effective ISMS documents
- URM Consultingthe guide to ISO 27001 risk assessment and the summary of the ISO 27002:2022 update
- CertiKitthe detailed walk-through of an ISO 27001 risk assessment
- NQA Certificationthe certification body's webinar on understanding the ISO 27001:2022 Annex A controls
- risk3sixtygetting ready for an ISO 27001 certification audit
- SoftComplythe webinar on implementing NIS2 alongside ISO 27001
- GRC Made Simplethe key differences between ISO 27001 and SOC 2
If you are one of these creators and would like a lesson removed or credited differently, write to info@wartens.com.